25732 粉丝
Models that come with $60 usage credits in Command Code GOAT.
· DeepSeek V4.1 Flash
· DeepSeek V4.1 Flash Fast
· GLM 5.3 Flash
· Kimi K3
Enjoy billions of tokens with the $10/mo GOAT plan
中文: 在 Command Code GOAT 中提供 60 美元使用积分的型号。
· DeepSeek V4.1 闪存
· DeepSeek V4.1 快速闪闪
GLM 5.3 闪光灯
· 基米 K3
使用每月10美元的GOAT计划享受数十亿枚代币
25732 粉丝
Use /add-dir to work across multiple directories in Command Code.
· Read and edit files outside your current project in accept-edits mode
· Great for separate frontend and API repos
$ npm i -g command-code
中文: 使用 /add-dir 在命令代码中跨多个目录工作。
以接受编辑模式在当前项目之外读取和编辑文件
非常适合独立的前端和API仓库
$ npm i -g 命令代码
🎬
视频
25732 粉丝
RT @CommandCodeAI: Free models live in Command Code right now.
· Space Bunny Alpha (with Max reasoning)
· Ling 3.1 Flash (increased 300 reqs/day)
· Ling 3.0 Flash Sante
· Laguna S 2.1
Y'all got some tokens to build for free.
25732 粉丝
Free models live in Command Code right now.
· Space Bunny Alpha (with Max reasoning)
· Ling 3.1 Flash (increased 300 reqs/day)
· Ling 3.0 Flash Sante
· Laguna S 2.1
Y'all got some tokens to build for free.
中文: 免费模型目前以命令代码为生。
· 太空兔子阿尔法(带 Max 推理)
· 凌3.1闪光灯(每天增加300次)
· 灵3.0闪光霖
拉古纳 S 2.1
你们都有一些免费的代币可以搭建。
25732 粉丝
RT @CommandCodeAI: Plan with one model
Implement with another
now live in Command Code
Your planning model explores the codebase and writes the plan. Approve it, and your implementation model takes over mid-run.
Set both in /config → Feature models https://twitter.com/CommandCodeAI/status/2106013581363782118/video/1
中文: RT @CommandCodeAI:使用一个模型进行规划
用另一个实现
现在使用命令代码
你的规划模型会探索代码库并编写计划。批准它,你的实现模型将占据中途运行。
将两者设置在 /config → 功能模型
🎬
视频
25732 粉丝
See complete announcement here.
https://x.com/CommandCodeAI/status/2105348821438067011
中文: 请参见此处的完整公告。
25732 粉丝
Remote Control is now live in both Command Code CLI and Desktop app.
中文: 远程控制现在同时在命令行代码CLI和桌面应用中都处于实时。
25732 粉丝
RT @CommandCodeAI: Ling 3.1 Flash (free model) just got an update.
We're increasing limits to 300 requests per day.
That means more tokens to build for free.
中文: RT @CommandCodeAI:Ling 3.1 Flash(免费型号)刚刚获得了更新。
我们每天增加300个请求的限额。
这意味着需要免费构建更多代币。
25732 粉丝
Read docs about choosing planning and implementation models.
https://commandcode.ai/docs/settings#planning-and-implementation-models
中文: 阅读文档,了解选择规划和实施模型的信息。
25732 粉丝
Plan with one model
Implement with another
now live in Command Code
Your planning model explores the codebase and writes the plan. Approve it, and your implementation model takes over mid-run.
Set both in /config → Feature models https://twitter.com/CommandCodeAI/status/2106013581363782118/video/1
中文: 用一个模型制定计划
用另一个实现
现在使用命令代码
你的规划模型会探索代码库并编写计划。批准它,你的实现模型将占据中途运行。
将两者设置在 /config → 功能模型
🎬
视频
25732 粉丝
RT @CommandCodeAI: We're increasing GLM 5.3 Flash to $60 credits in Command Code.
Get 6x usage on GOAT plan
· 1M context window
· Multimodal (text, image, video)
· Fast coding +long-horizon agent tasks
🐐
中文: RT @CommandCodeAI:我们将 GLM 5.3 Flash 的 Command Code 积分增加至 60 美元。
获取 GOAT 计划的 6 次使用
1M 上下文窗口
多模态(文字、图片、视频)
快速编码+长激素代理任务
🐐
25732 粉丝
Ling 3.1 Flash (free model) just got an update.
We're increasing limits to 300 requests per day.
That means more tokens to build for free.
中文: Ling 3.1 Flash(免费型号)刚刚获得了更新。
我们每天增加300个请求的限额。
这意味着需要免费构建更多代币。
25732 粉丝
We're increasing GLM 5.3 Flash to $60 credits in Command Code.
Get 6x usage on GOAT plan
· 1M context window
· Multimodal (text, image, video)
· Fast coding +long-horizon agent tasks
🐐
中文: 我们将 GLM 5.3 Flash 的 Command Code 额度提高到 60 美元。
获取 GOAT 计划的 6 次使用
1M 上下文窗口
多模态(文字、图片、视频)
快速编码+长激素代理任务
🐐
25732 粉丝
Space Bunny Alpha continues to be free in Command Code.
Now faster, with better throughput and reliability
1M context. Multimodal. Till Oct 5 on all plans
中文: 太空兔女性阿尔法在命令代码中仍然免费。
现在速度更快,具有更高的吞吐量和可靠性
1M 上下文。多模态。至10月5日所有计划
25732 粉丝
RT @CommandCodeAI: We're increasing Kimi K3 usage to $60 credits in Command Code GOAT.
For the next 7 days, get 6x usage for Kimi K3.
· 1M token context window
· Multimodal (text, image, reasoning)
· For long-horizon coding and knowledge work
🐐
中文: RT @CommandCodeAI:我们将使用 Kimi K3 的 Command Code GOAT 额度提高到 60 美元。
在接下来的7天内,使用6次即可使用 Kimi K3。
1M 令牌上下文窗口
多模态(文本、图像、推理)
· 用于长时间的编程和知识工作
🐐
25732 粉丝
We're increasing Kimi K3 usage to $60 credits in Command Code GOAT.
For the next 7 days, get 6x usage for Kimi K3.
· 1M token context window
· Multimodal (text, image, reasoning)
· For long-horizon coding and knowledge work
🐐
中文: 我们将使用 Kimi K3 的 Command Code GOAT 额度提高到 60 美元。
在接下来的7天内,使用6次即可使用 Kimi K3。
1M 令牌上下文窗口
多模态(文本、图像、推理)
· 用于长时间的编程和知识工作
🐐
25732 粉丝
RT @CommandCodeAI: Ling 3.1 Flash is now free in Command Code.
· 560B total params. 25B active params
· available all plans. all subs
🐐
25732 粉丝
Remote Control now available in Command Code.
· Run /rc to open your session in Telegram or Discord
· Message from your phone and get live responses
· Sessions keep running on your laptop
Control Command Code with your mobile
中文: 远程控制现在可在命令代码中使用。
运行 /rc 以在 Telegram 或 Discord 中打开您的会话
· 通过手机留言并获取实时回复
· 会话在您的笔记本电脑上持续运行
使用您的手机控制命令代码
🎬
视频
25732 粉丝
Read docs to learn more how Remote Control works.
https://commandcode.ai/docs/rc
中文: 阅读文档,了解远程控制的工作原理。
25732 粉丝
RT @CommandCodeAI: Read BYOK docs to learn more:
https://commandcode.ai/docs/byok#open-ai-chat-gpt-codex
中文: RT @CommandCodeAI:阅读 BYOK 文档以了解更多信息:
25732 粉丝
RT @CommandCodeAI: Ling 3.1 Flash is now free in Command Code.
· 560B total params. 25B active params
· available all plans. all subs
🐐
中文: RT @CommandCodeAI:Ling 3.1 Flash 现已在命令代码中免费。
总共560B段。25B 活性参数
所有计划都可用。所有子
🐐
25732 粉丝
Ling 3.1 Flash is now free in Command Code.
· 560B total params. 25B active params
· available all plans. all subs
🐐
中文: Ling 3.1 Flash 现已在命令代码中免费。
总共560B段。25B 活性参数
所有计划都可用。所有子
🐐
25732 粉丝
RT @CommandCodeAI: GPT 6.1 Sol is now live in Command Code.
Astra-level intelligence at one-fifth price and 95% cache read.
Available on Max and API.
中文: RT @CommandCodeAI:GPT 6.1 Sol 现已在命令代码中上线。
以五分之一的价格读取的Astra级智能和95%的缓存。
可在 Max 和 API 上使用。
25732 粉丝
@OpenAI Live in @CommandCodeAI yay!! 🐐
中文: @OpenAI 实时在线 @CommandCodeAI ayay!!🐐
25732 粉丝
GPT 6.1 Sol is now live in Command Code.
Astra-level intelligence at one-fifth price and 95% cache read.
Available on Max and API.
中文: GPT 6.1 Sol 现已采用命令代码。
以五分之一的价格和95%的缓存读取的Astra级智能。
可在 Max 和 API 上使用。
25732 粉丝
Read BYOK docs to learn more:
https://commandcode.ai/docs/byok#open-ai-chat-gpt-codex
中文: 阅读BYOK文档以了解更多信息:
25732 粉丝
You can now use your ChatGPT subscription in Command Code.
· Run /connect to link your account
· Requests run locally from the CLI
· GPT models get their own section in /model
Try now: $ npm i -g command-code
25732 粉丝
DeepSeek V4.1 Flash Fast is live with $60 usage credits in Command Code GOAT. 🐐
· 250-300 TPS high speed and throughput
· 1M context · full weight as always
Billions of tokens at 2-3x the speed.
中文: DeepSeek V4.1 Flash Fast 在 Command Code GOAT 中提供 60 美元的使用额度。🐐
250-300 TPS 高速和高吞吐量
· 1M 上下文 · 一如既往的满重
数十亿枚代币的速度是两亿倍。
25732 粉丝
RT @CommandCodeAI: Command Code now supports OpenAI Responses API.
· 98 open and closed models
· Function and custom tools stay client-side
· Built-in tools pass through when supported
𝙿𝙾𝚂𝚃 𝚑𝚝𝚝𝚙𝚜://𝚊𝚙𝚒.𝚌𝚘𝚖𝚖𝚊𝚗𝚍𝚌𝚘𝚍𝚎.𝚊𝚒/𝚙𝚛𝚘𝚟𝚒𝚍𝚎𝚛/𝚟𝟷/𝚛𝚎𝚜𝚙𝚘𝚗𝚜𝚎𝚜
中文: RT @CommandCodeAI:命令代码现在支持 OpenAI 响应 API。
98 个开放式和封闭式型号
功能和自定义工具保持客户端
支持内置工具通过
发布
25732 粉丝
Claude Sonnet 5.5 is now live in Command Code.
· Runs 30% faster, costs 30% less
· Beats Opus 5.5 on Terminal-Bench 4.0
Available across GOAT, Pro, Max and API.
中文: 克劳德·索内特5.5现在以《命令代码》为名。
跑步速度快30%,成本低30%
· 在终端-长队4.0上击败Opus 5.5
可在 GOAT、Pro、Max 和 API 上使用。
25732 粉丝
Try now with Provider API on GOAT plan and above! https://commandcode.ai/provider
中文: 立即使用 Provider API 获取 GOAT 计划及以上内容!
25732 粉丝
Command Code now supports OpenAI Responses API.
· 98 open and closed models
· Function and custom tools stay client-side
· Built-in tools pass through when supported
𝙿𝙾𝚂𝚃 𝚑𝚝𝚝𝚙𝚜://𝚊𝚙𝚒.𝚌𝚘𝚖𝚖𝚊𝚗𝚍𝚌𝚘𝚍𝚎.𝚊𝚒/𝚙𝚛𝚘𝚟𝚒𝚍𝚎𝚛/𝚟𝟷/𝚛𝚎𝚜𝚙𝚘𝚗𝚜𝚎𝚜
中文: Command Code 现在支持 OpenAI 响应 API。
98 个开放式和封闭式型号
功能和自定义工具保持客户端
支持内置工具通过
发布
25732 粉丝
RT @CommandCodeAI: We're making $60 usage on DeepSeek V4.1 Flash now permanent in Command Code GOAT.
Happy Sunday!
🐐
中文: RT @CommandCodeAI:我们现在在 Command Code GOAT 中永久使用 DeepSeek V4.1 Flash 时,使用价格为 60 美元。
星期天快乐!
🐐
25732 粉丝
RT @CommandCodeAI: We're making $60 usage on DeepSeek V4.1 Flash now permanent in Command Code GOAT.
Happy Sunday!
🐐
中文: RT @CommandCodeAI:我们现在在 Command Code GOAT 中永久使用 DeepSeek V4.1 Flash 时,使用价格为 60 美元。
星期天快乐!
🐐
25732 粉丝
RT @CommandCodeAI: We're making $60 usage on DeepSeek V4.1 Flash now permanent in Command Code GOAT.
Happy Sunday!
🐐
中文: RT @CommandCodeAI:我们现在在 Command Code GOAT 中永久使用 DeepSeek V4.1 Flash 时,使用价格为 60 美元。
星期天快乐!
🐐
25732 粉丝
RT @CommandCodeAI: We're making $60 usage on DeepSeek V4.1 Flash now permanent in Command Code GOAT.
Happy Sunday!
🐐
25732 粉丝
We're making $60 usage on DeepSeek V4.1 Flash now permanent in Command Code GOAT.
Happy Sunday!
🐐
中文: 我们现在在 Command Code GOAT 中永久使用 DeepSeek V4.1 Flash 时,使用价格为 60 美元。
星期天快乐!
🐐
25732 粉丝
Free models live in Command Code right now.
· Pixel Canary (stealth) 🆕
· Space Bunny Alpha (stealth)
· Ling 3.0 Flash Sante
· Laguna S 2.1
Available to all subscribers, on every plan.
中文: 免费模型目前以命令代码为生。
· 像素金丝雀(隐身)🆕
太空兔阿尔法(隐身)
· 灵3.0闪光霖
拉古纳 S 2.1
所有订阅者,每条方案都提供。
25732 粉丝
RT @CommandCodeAI: Pixel Canary is live, new free stealth model.
$ 𝚗𝚙𝚖 𝚒 -𝚐 𝚌𝚘𝚖𝚖𝚊𝚗𝚍-𝚌𝚘𝚍𝚎@𝚕𝚊𝚝𝚎𝚜𝚝
/model pixel-canary (free)
Response speed at ~20-25 tps.
中文: RT @CommandCodeAI:Pixel Canary 是实时的,全新的免费隐身型号。
$ npm i -g 命令代码@latest
/模型像素-任意(免费)
响应速度约为20-25 tps。
25732 粉丝
RT @CommandCodeAI: Pixel Canary is live, new free stealth model.
$ 𝚗𝚙𝚖 𝚒 -𝚐 𝚌𝚘𝚖𝚖𝚊𝚗𝚍-𝚌𝚘𝚍𝚎@𝚕𝚊𝚝𝚎𝚜𝚝
/model pixel-canary (free)
Response speed at ~20-25 tps.
中文: RT @CommandCodeAI:Pixel Canary 是实时的,全新的免费隐身型号。
$ npm i -g 命令代码@latest
/模型像素-任意(免费)
响应速度约为20-25 tps。
25732 粉丝
Pixel Canary is live, new free stealth model.
$ 𝚗𝚙𝚖 𝚒 -𝚐 𝚌𝚘𝚖𝚖𝚊𝚗𝚍-𝚌𝚘𝚍𝚎@𝚕𝚊𝚝𝚎𝚜𝚝
/model pixel-canary (free)
Response speed at ~20-25 tps.
中文: Pixel Canary 是一款全新的免费隐身型。
$ npm i -g 命令代码@latest
/模型像素-任意(免费)
响应速度约为20-25 tps。
25732 粉丝
New in Command Code: /loop command
Run a task, then repeat it on a fixed or self-paced schedule until the job is done.
Try now: $ npm i -g command-code https://twitter.com/CommandCodeAI/status/2103567725356531852/video/1
中文: 命令代码中的新代码:/循环命令
运行一个任务,然后按照固定或自定进度的时间进行重复,直到任务完成。
立即试用:$ npm i -g 命令代码
🎬
视频
25732 粉丝
Free models live in Command Code right now.
· Space Bunny Alpha
· Ling 3.0 Flash Sante
· Laguna S 2.1
Available to all subscribers, on every plan.
中文: 免费模型目前以命令代码为生。
太空兔阿尔法
· 灵3.0闪光霖
拉古纳 S 2.1
所有订阅者,每条方案都提供。
25732 粉丝
RT @MrAhmadAwais: Command Code is #1 on Vercel Gateway.
We launched in May. First coding agent purpose built for open models. Check what happens in July/Aug in the chart below.
In Aug we launched v1 and $10 GOAT plan.
53K active paying customers now.
We're just getting started.
中文: RT @MrAhmadAwais:命令行代码在 Vercel Gateway 上排名第一。
我们于五月启动。专为开放模型构建的首个编码代理。请在下图中查看7月/8月的情况。
8月,我们推出了v1和10美元的GOAT计划。
现为53K名活跃付费客户。
我们才刚刚开始。
25732 粉丝
RT @CommandCodeAI: You can now use Shift+Tab to bypass permissions.
· Switch mid-session
· No need to restart with cmd --yolo https://twitter.com/CommandCodeAI/status/2103154871335788818/video/1
中文: RT @CommandCodeAI:现在可以使用 Shift+Tab 来绕过权限。
· 切换中段
无需使用cmd -yolo
🎬
视频
25732 粉丝
You can now use Shift+Tab to bypass permissions.
· Switch mid-session
· No need to restart with cmd --yolo https://twitter.com/CommandCodeAI/status/2103154871335788818/video/1
中文: 现在可以使用 Shift+Tab 来绕过权限。
· 切换中段
无需使用cmd -yolo
🎬
视频
25732 粉丝
RT @CommandCodeAI: We’ve shipped 12 new models in Command Code.
Here's a quick recap for y'all.
· Mimo V2.6 Flash
· Mimo V2.6 Pro
· DeepSeek V4.1 Flash (ext. usage)
· Jev (free)
· GPT 6 Luna
· GPT 6 Sol
· Grok 4.7
· Mimo V2.6 Pro Ultraspeed
· GLM 5.3 FlashX
· Qwen 3.8 Omni Flash
· Opus 5.5
· Step 5 Preview
中文: RT @CommandCodeAI:我们已以命令代码发布了12款新型号。
以下是你们所有人的快速回顾。
· Mimo V2.6 闪存
· Mimo V2.6 Pro
· DeepSeek V4.1 闪存(使用外)
杰夫(免费)
· GPT 6 卢娜
· 盖普6索尔
· 格鲁克 4.7
· Mimo V2.6 Pro 超速
· GLM 5.3 FlashX
Qwen 3.8 全闪存
· Opus 5.5
· 步骤5预览
25732 粉丝
RT @CommandCodeAI: Space Bunny Alpha (stealth model) is now free in Command Code.
1M context. Multimodal. Available all plans
中文: RT @CommandCodeAI:太空兔子阿尔法(隐身模型)现已在命令代码中免费。
1M 上下文。多模态。所有计划可用
25732 粉丝
Space Bunny Alpha (stealth model) is now free in Command Code.
1M context. Multimodal. Available all plans
25732 粉丝
RT @CommandCodeAI: We’ve shipped 12 new models in Command Code.
Here's a quick recap for y'all.
· Mimo V2.6 Flash
· Mimo V2.6 Pro
· DeepSeek V4.1 Flash (ext. usage)
· Jev (free)
· GPT 6 Luna
· GPT 6 Sol
· Grok 4.7
· Mimo V2.6 Pro Ultraspeed
· GLM 5.3 FlashX
· Qwen 3.8 Omni Flash
· Opus 5.5
· Step 5 Preview
中文: RT @CommandCodeAI:我们已以命令代码发布了12款新型号。
以下是你们所有人的快速回顾。
· Mimo V2.6 闪存
· Mimo V2.6 Pro
· DeepSeek V4.1 闪存(使用外)
杰夫(免费)
· GPT 6 卢娜
· 盖普6索尔
· 格鲁克 4.7
· Mimo V2.6 Pro 超速
· GLM 5.3 FlashX
Qwen 3.8 全闪存
· Opus 5.5
· 步骤5预览
25732 粉丝
RT @CommandCodeAI: Tested Mimo-V2.6-Flash, Grok-4.7, and DeepSeek-V4.1-Flash with 3D SubwayBench using the same /design prompt.
🔹 DSV4.1-Flash: 9/10 · $0.024 · one-shot · strong 3D UI/UX + gameplay
🔹 Mimo-V2.6-Flash: 8/10 · $0.018 · playable 2D result in ~4 iterations
🔹 Grok 4.7: 3/10 · $0.35 · slower UI + gameplay, needs more iteration
中文: RT @CommandCodeAI:使用相同的/设计提示测试了Mimo-V2.6-Flash、Grok-4.7和DeepSeek-V4.1-Flash。
🔹 DSV4.1-Flash:9/10 · 0.024美元 · 单拍 · 强大的3D UI/UX+游戏体验
🔹 Mimo-V2.6-Flash:8/10 · 0.018美元 · 可玩2D结果,约4次迭代
🔹 Grok 4.7:3/10 · 0.35 美元 · 更慢的 UI + 游戏玩法,需要更多迭代
🎬
视频
25732 粉丝
We’ve shipped 12 new models in Command Code.
Here's a quick recap for y'all.
· Mimo V2.6 Flash
· Mimo V2.6 Pro
· DeepSeek V4.1 Flash (ext. usage)
· Jev (free)
· GPT 6 Luna
· GPT 6 Sol
· Grok 4.7
· Mimo V2.6 Pro Ultraspeed
· GLM 5.3 FlashX
· Qwen 3.8 Omni Flash
· Opus 5.5
· Step 5 Preview
中文: 我们已在命令码中出货了12款新型号。
以下是你们所有人的快速回顾。
· Mimo V2.6 闪存
· Mimo V2.6 Pro
· DeepSeek V4.1 闪存(使用外)
杰夫(免费)
· GPT 6 卢娜
· 盖普6索尔
· 格鲁克 4.7
· Mimo V2.6 Pro 超速
· GLM 5.3 FlashX
Qwen 3.8 全闪存
· Opus 5.5
· 步骤5预览
25732 粉丝
RT @CommandCodeAI: Jev is free in Command Code! 🐐
中文: RT @CommandCodeAI:Jev 在命令代码中免费!🐐
25732 粉丝
RT @CommandCodeAI: GPT 6 Sol and Luna are live in Command Code.
Luna is available on all plans and API
E.g. in $10 GOAT plan: ~30K reqs, ~1.5B tokens
Sol is available on Pro, Max and API
中文: RT @CommandCodeAI:GPT 6 Sol 和 Luna 以命令代码为名。
Luna 可在所有计划和 API 上使用
例如,每10美元的GOAT套餐:约3万雷克斯,约1.5亿美元代币
Sol 可在 Pro、Max 和 API 上使用
25732 粉丝
RT @CommandCodeAI: Tested Mimo-V2.6-Flash, Grok-4.7, and DeepSeek-V4.1-Flash with 3D SubwayBench using the same /design prompt.
🔹 DSV4.1-Flash: 9/10 · $0.024 · one-shot · strong 3D UI/UX + gameplay
🔹 Mimo-V2.6-Flash: 8/10 · $0.018 · playable 2D result in ~4 iterations
🔹 Grok 4.7: 3/10 · $0.35 · slower UI + gameplay, needs more iteration
中文: RT @CommandCodeAI:使用相同的/设计提示测试了Mimo-V2.6-Flash、Grok-4.7和DeepSeek-V4.1-Flash。
🔹 DSV4.1-Flash:9/10 · 0.024美元 · 单拍 · 强大的3D UI/UX+游戏体验
🔹 Mimo-V2.6-Flash:8/10 · 0.018美元 · 可玩2D结果,约4次迭代
🔹 Grok 4.7:3/10 · 0.35 美元 · 更慢的 UI + 游戏玩法,需要更多迭代
🎬
视频
25732 粉丝
Our engineering and design team has been testing 26+ side-by-side comparisons across frontier and open models. All runs are public and open source. Benchmark for this demo here:
https://github.com/CommandCodeAI/slash-design-showcase/tree/main/subway-surfers
中文: 我们的工程与设计团队一直在前沿和开放式模型上测试26个并排对比。所有运行均为公开和开源。此演示的基准:
25732 粉丝
Tested Mimo-V2.6-Flash, Grok-4.7, and DeepSeek-V4.1-Flash with 3D SubwayBench using the same /design prompt.
🔹 DSV4.1-Flash: 9/10 · $0.024 · one-shot · strong 3D UI/UX + gameplay
🔹 Mimo-V2.6-Flash: 8/10 · $0.018 · playable 2D result in ~4 iterations
🔹 Grok 4.7: 3/10 · $0.35 · slower UI + gameplay, needs more iteration
中文: 使用相同的/设计提示,使用3D SubwayBench测试了Mimo-V2.6-Flash、Grok-4.7和DeepSeek-V4.1-Flash。
🔹 DSV4.1-Flash:9/10 · 0.024美元 · 单拍 · 强大的3D UI/UX+游戏体验
🔹 Mimo-V2.6-Flash:8/10 · 0.018美元 · 可玩2D结果,约4次迭代
🔹 Grok 4.7:3/10 · 0.35 美元 · 更慢的 UI + 游戏玩法,需要更多迭代
🎬
视频
25732 粉丝
GPT 6 Sol and Luna are live in Command Code.
Luna is available on all plans and API
E.g. in $10 GOAT plan: ~30K reqs, ~1.5B tokens
Sol is available on Pro, Max and API
中文: GPT 6 Sol 和 Luna 以命令代码为名。
Luna 可在所有计划和 API 上使用
例如,每10美元的GOAT套餐:约3万雷克斯,约1.5亿美元代币
Sol 可在 Pro、Max 和 API 上使用
25732 粉丝
Claude Opus 5.5 is live in Command Code Max and API.
中文: Claudei Opus 5.5 在 Command Code Max 和 API 中实时使用。
25732 粉丝
RT @MrAhmadAwais: Launching Jev on Command Code for free today.
Jev x Command Code is super interesting.
You can only use Jev in headless mode or Provider API.
Also open sourced a mod "cmd-mod-jev-nudge"
Use Jev for free to keep your agent running as long as the there's more work to do.
🎬
视频
25732 粉丝
Command Code supports Git worktrees.
Use /worktree to create or switch and run parallel sessions, each on its own branch. https://twitter.com/CommandCodeAI/status/2102434616770756638/video/1
中文: 命令代码支持 Git 工作树。
使用 /worktree 创建或切换并运行并行会话,每个会话都在其自己的分支上。
🎬
视频
25732 粉丝
RT @CommandCodeAI: Grok 4.7 is now live in Command Code.
40% for the next 7 days
$35 credits (3.5x usage) in GOAT
Available on GOAT, Pro, Max, and via API.
🐐
25732 粉丝
Step 5 Preview is now live in Command Code.
Available across all plans and API.
中文: 步骤5预览现在以命令代码为现名。
适用于所有计划和API。
25732 粉丝
Grok 4.7 is now live in Command Code.
40% for the next 7 days
$35 credits (3.5x usage) in GOAT
Available on GOAT, Pro, Max, and via API.
🐐
中文: Grok 4.7 现已进入命令代码。
未来7天为40%
山羊积分35美元(使用量3.5倍)
可在 GOAT、Pro、Max 和 API 上使用。
🐐
25732 粉丝
RT @CommandCodeAI: MiMo V2.6 Pro & Flash are live in Command Code 🐐
Available on all plans.
Command Code has the best usage in market for both models.
E.g. in $10 GOAT plan:
• MiMo-V2.6 Flash $67 (6.7x usage) for 72hrs
• MiMo-V2.6 Pro $20 (2x usage)
🐐
中文: RT @CommandCodeAI:MiMo V2.6 Pro & Flash 以命令代码为实时版本 🐐
可在所有计划中使用。
Command Code 对两种型号的市场使用率都最佳。
例如,10美元GOAT套餐:
• 72小时用于MiMo-V2.6 闪光灯 67美元(6.7倍)
• MiMo-V2.6 Pro 20美元(使用时间)
🐐
25732 粉丝
MiMo V2.6 Pro & Flash are live in Command Code 🐐
Available on all plans.
Command Code has the best usage in market for both models.
E.g. in $10 GOAT plan:
• MiMo-V2.6 Flash $67 (6.7x usage) for 72hrs
• MiMo-V2.6 Pro $20 (2x usage)
🐐
中文: MiMo V2.6 Pro & Flash 以命令代码为实时版本 🐐
可在所有计划中使用。
Command Code 对两种型号的市场使用率都最佳。
例如,10美元GOAT套餐:
• 72小时用于MiMo-V2.6 闪光灯 67美元(6.7倍)
• MiMo-V2.6 Pro 20美元(使用时间)
🐐
25732 粉丝
Beware of reverse engineered proxy scams.
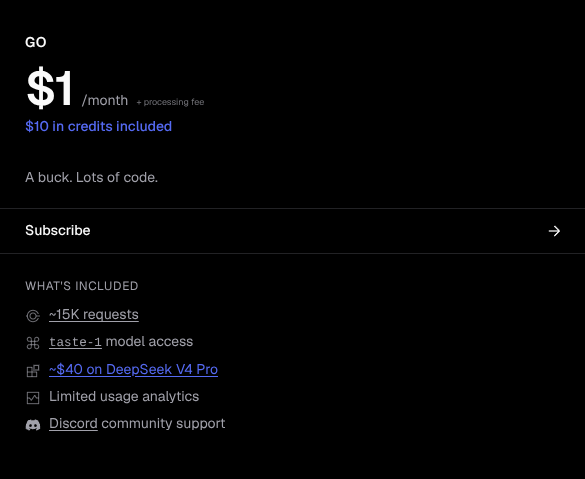
Last week we caught a fraud ring that created ~40K fake accounts on our $1 Go plan and tried to push ~$450K of inference through them. We banned and reported every account and cut off their proxies.
The $1 Go plan has helped thousands of students, developers, non-profits, and hobbyists get started with the Command Code harness and open models for almost nothing.
We subsidize it on purpose, and we're going to keep it as long as we can. Stopping fraud is how we make sure it stays available to the people it was built for.
This isn't unique to Command Code. Stripe, OpenRouter, OpenCode, and Cline have all banned hundreds of thousands of fake accounts and proxies. We believe it's the same crew moving from platform to platform, and the proxies we shut down are a few of many.
How the proxy fraud works:
the ring used unofficial reverse engineered proxies, including open source ones, to plug bulk created accounts into automated pipelines, drain the subsidy, resell it, and harvest user data along the way.
Do NOT trust unofficial proxies or providers. Even if they look clean, even when open source, they can update and turn malicious at any time.
If you're using one of these proxies: the tokens come from farmed accounts your prompts, code, and keys may pass through servers run by people who committed fraud to get them. And a proxy between your harness and the model can inject fake tool calls that read files, run commands, or exfiltrate data.
Use official channels: the Command Code harness, CLI, Desktop app, or the official provider API (included on GOAT and above plans). Never hand your credentials to an unofficial service, no matter how legit it looks.
If you want Command Code inference inside another harness, reach out to us.
We're also building official provider packages so you don't need a third party one. Starting with Command Code provider for Pi today.
We don't tolerate fraud and will take every action needed to protect the platform and our users.
We're on a mission to make AI accessible to everyone, regardless of their background or resources. Open models with excellent harness and inference engineering enable us to do that safely and sustainably.
中文: 警惕反向工程代理诈骗。
上周,我们发现了一个诈骗团伙,该团伙在1美元的“Go计划中”,创建了约4万个虚假账户,并试图通过这些骗局推动约45万美元的推断。我们封禁并举报了所有账户,并切断了他们的代理账号。
1美元的Go计划已帮助成千上万的学生、开发者、非营利组织和业余爱好者开始使用Command Code 线束,并几乎一无所获地打开模型。
我们故意补贴它,并且会尽可能保持它。制止欺诈是确保其为人们提供可供使用的方式。
这并非命令行代码独有。Stripe、OpenRouter、OpenCode 和 Cline 已全部封禁了数十万个虚假账户和代理账号。我们相信,从平台到平台的团队是相同的,而我们关闭的代理团队也是众多代理团队中的少数。
代理欺诈的运作原理:
该团伙使用非官方的反向工程代理,包括开源代理,将大量创建的账户插入自动化管道中,耗尽补贴,转售,并在此过程中收集用户数据。
不要信任非官方代理或服务提供商。即使它们看起来干净,即使开源时,也可以随时更新并变成恶意。
如果你使用的是这些代理之一:这些令牌来自养殖账户,你的提示、代码和密钥可能会通过由实施欺诈的人运行的服务器来获取这些提示。使用您的线束和模型之间的代理可以注入虚假的工具调用,用于读取文件、运行命令或泄露数据。
使用官方渠道:命令行代码线束、CLI、桌面应用或官方服务提供商API(包含在GOAT及以上套餐中)。无论凭据多么合法,都不要将凭据交给非官方服务。
如果想在另一个线束内进行命令代码推断,请与我们联系。
我们还在构建官方服务提供商套餐,因此您无需第三方。从今天开始为 Pi 提供命令代码。
我们不容忍欺诈行为,将采取一切必要措施来保护平台和用户。
我们的使命是让每个人,无论其背景或资源如何,都能让人工智能变得便捷。采用出色的线束和推理工程的开放式模型,使我们能够安全且可持续地实现这一技术。
25732 粉丝
RT @CommandCodeAI: Extending $60 usage on DeepSeek V4.1 Flash another 8 days. 🐐
25732 粉丝
Extending $60 usage on DeepSeek V4.1 Flash another 8 days. 🐐
中文: 将 DeepSeek V4.1 Flash 的 60 美元使用时间再延长 8 天。🐐
25732 粉丝
@YogaDharma21 Update: we’re back thank you for the patience.
中文: @YogaDharma21 更新:我们回来感谢您的耐心。
25732 粉丝
@YogaDharma21 Fix is on the way. Please bear with us.
中文: @YogaDharma21 修复正在进行中。请忍受我们。
25732 粉丝
RT @CommandCodeAI: Ran FlappyBench on Qwen3.8-Omni-Flash, DeepSeek-V4.1-Flash, and Gemini 3.8 Flash with the same design prompt.
🔹 Qwen 3.8 Omni Flash: 9/10 · $0.013 · smooth gameplay and cheaper
🔹 DS V4.1 Flash: 9/10 · $0.0089 one-shot with the lowest cost
🔹 Gemini 3.8 Flash: 5/10 · $0.205 · 4-5 iterations but still hard-coded gameplay and costs 23x more
🎬
视频
25732 粉丝
Our engineering and design team has been testing 26+ side-by-side comparisons across frontier and open models. All runs are public and open source. Benchmark for this demo here:
https://github.com/CommandCodeAI/slash-design-showcase/tree/main/flappy-bird
中文: 我们的工程与设计团队一直在前沿和开放式模型上测试26个并排对比。所有运行均为公开和开源。此演示的基准:
25732 粉丝
Ran FlappyBench on Qwen3.8-Omni-Flash, DeepSeek-V4.1-Flash, and Gemini 3.8 Flash with the same design prompt.
🔹 Qwen 3.8 Omni Flash: 9/10 · $0.013 · smooth gameplay and cheaper
🔹 DS V4.1 Flash: 9/10 · $0.0089 one-shot with the lowest cost
🔹 Gemini 3.8 Flash: 5/10 · $0.205 · 4-5 iterations but still hard-coded gameplay and costs 23x more
中文: 采用相同设计提示的 Qwen3.8-Omni-Flash、DeepSeek-V4.1-Flash 和 Gemini 3.8 Flash 的 FlappyBench 功能。
🔹 Qwen 3.8 Omni Flash:9/10 · 0.013美元 · 流畅的玩法和更便宜的
🔹 DS V4.1 闪光灯:9/10 · 0.0089美元,单发单发成本最低
🔹 Gemini 3.8 闪光灯:5/10 · 0.205 美元 · 4-5 次迭代,但仍使用硬编码,且价格超过 23 倍
🎬
视频
25732 粉丝
RT @btsouth: I owe @CommandCodeAI a shoutout.
I’ve been posting a lot about how good DeepSeek V4.1 Flash is, but I’d mostly been using it through Hermes with Command Code as a provider.
I finally tried Command Code’s own harness.
The difference is ridiculous.
Same V4.1 Flash, but responses feel dramatically faster and the whole experience is much more immediate.
Hermes is great for long-running autonomous work, but Command Code feels so much better for interactive coding and quick back-and-forth.
The desktop app seems great so far too.
I seriously underestimated how much the harness changes the experience.
中文: RT @btsouth:我欠@CommandCodeAI一个喊叫。
我一直在发布大量关于DeepSeek V4.1 Flash的优秀信息,但我主要通过Hermes与Command Code作为服务提供商进行使用。
我终于尝试了Command Code自己的安全带。
差别太荒谬了。
相同的V4.1闪存,但响应速度明显更快,整体体验也更加即时。
爱马仕非常适合长期自主工作,但《命令代码》在交互式编程和快速的反复工作中感觉要出色得多。
这款桌面应用到目前为止似乎也很棒。
我严重低估了线束对体验的改变程度。
25732 粉丝
RT @MrAhmadAwais: Command Code is fastest DeepSeek inference in the world.
Better
Faster
Cheaper
All the work we put into tool repairs have and harness + inference engineering is paying dividends now.
Our mission is to be inference-native.
Let's go, GOAT 🐐
25732 粉丝
GLM-5.3 FlashX is now live in Command Code.
· High speed variant of GLM-5.3 Flash
· ~200 TPS with 1M context window
· Multimodal (text, image, video)
Available across all plans and API.
中文: GLM-5.3 FlashX 现已在命令代码中上线。
· GLM-5.3 闪光灯的高速变速器
约200个带1米上下文窗口的TPS
多模态(文字、图片、视频)
适用于所有计划和API。
25732 粉丝
Qwen 3.8 Omni Flash is now live in Command Code.
Available across all plans and API.
中文: Qwen 3.8 Omni Flash 现已在命令代码中上线。
适用于所有计划和API。
25732 粉丝
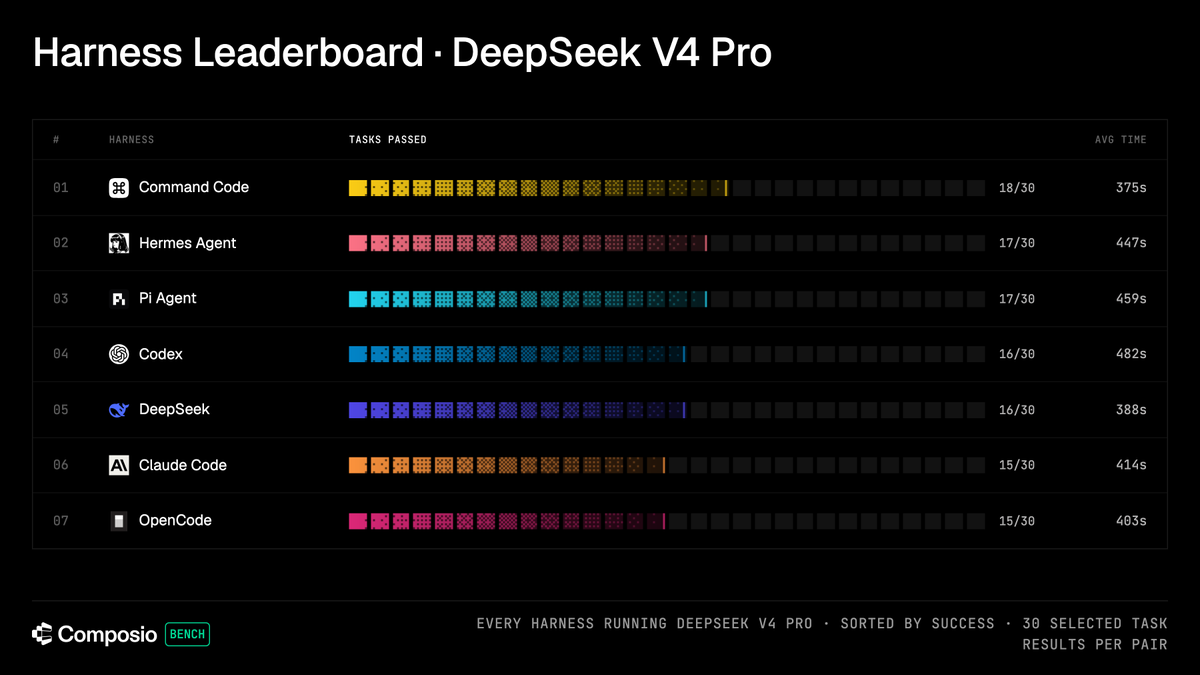
RT @MrAhmadAwais: Command Code outperformed every other harness on open models like DeepSeek in Composio's bench. 🐐
🔹 Most accurate: Solved 18/30 tasks
🔹 Fastest avg time per tasks: 375s
Beating even DeepSeek's own harness. https://twitter.com/MrAhmadAwais/status/2100650460797616636/photo/1

25732 粉丝
RT @fkadev: I’m trying out the @CommandCodeAI macOS app released yesterday. It didn't have a "Computer Use" feature initially, so I asked it to use an open-source tool to handle that functionality (DeepSeek 4.1 Flash). And it created an MCP server for UI-TARS, wrote its own computer-use capability, and is now working flawlessly. Although it’s a bit slower compared to Codex and Claude, but man it is incredibly cheap.
Here is a screenshot showing it playing XOX on Google:
中文: RT @fkadev:我正在尝试昨天发布的 @CommandCodeAI macOS 应用。最初没有“计算机使用”功能,因此我要求它使用开源工具来处理该功能(DeepSeek 4.1 Flash)。它为UI-TARS创建了一个MCP服务器,编写了自己的计算机使用功能,并且现在运行得无瑕。虽然与Codex和Claude相比有点慢,但确实非常便宜。
以下是一张显示其在谷歌上播放XOX的截图:

25732 粉丝
RT @CommandCodeAI: Stop copy-pasting errors. IDE diagnostics are quite strong.
Open Command Code. Select your code. Type fix this https://twitter.com/CommandCodeAI/status/2100566737771233361/video/1
中文: RT @CommandCodeAI:停止复制粘贴错误。IDE 诊断功能相当强大。
开放命令代码。选择你的代码。输入修复此
🎬
视频
25732 粉丝
Stop copy-pasting errors. IDE diagnostics are quite strong.
Open Command Code. Select your code. Type fix this https://twitter.com/CommandCodeAI/status/2100566737771233361/video/1
中文: 停止复制粘贴错误。IDE 诊断功能相当强大。
开放命令代码。选择你的代码。输入修复此
🎬
视频
25732 粉丝
RT @MrAhmadAwais: Command Code is one of the most token efficient top tier harnesses - leading accuracy, cost, and speed for both open and closed frontier models!!
25732 粉丝
RT @CommandCodeAI: Introducing Command Code Desktop App! ⌘
Available today in beta for Mac, Linux, & Windows.
Building the most powerful agentic app, starting with code. Multiple agents, files, Git, terminal, browser previews, plans, and instant edits with /design.
This is just the beginning.
🎬
视频
25732 粉丝
We have a massive roadmap ahead. Computer use, sandboxes, cloud computers, and a couple of secret projects coming next!
Download the desktop app and get started: https://commandcode.ai/desktop
中文: 我们前方有一条庞大的路线图。计算机使用、沙盒、云计算机,以及接下来将推出的几个秘密项目!
下载桌面应用程序并开始:
25732 粉丝
Introducing Command Code Desktop App! ⌘
Available today in beta for Mac, Linux, & Windows.
Building the most powerful agentic app, starting with code. Multiple agents, files, Git, terminal, browser previews, plans, and instant edits with /design.
This is just the beginning.
🎬
视频
25732 粉丝
RT @MrAhmadAwais: Super excited for the launch tomorrow. https://twitter.com/MrAhmadAwais/status/2100112592543101107/photo/1
25732 粉丝
RT @CommandCodeAI: Mods are more powerful than plugins.
Command Code can build mods and modify any behavior from programmatic hooks to a completely different inference provider.
We bet you haven’t experienced something as powerful before.
Build a mod now and make Command Code do anything you want.
中文: RT @CommandCodeAI:模组比插件更强大。
Command Code 可以构建模组,并将从编程钩子到完全不同的推理提供程序的任何行为进行修改。
我们以为你以前从未体验过那么强大的东西。
立即构建一个模组,让命令代码做到任何你想做的事情。
🎬
视频
25732 粉丝
RT @CommandCodeAI: Mods are more powerful than plugins.
Command Code can build mods and modify any behavior from programmatic hooks to a completely different inference provider.
We bet you haven’t experienced something as powerful before.
Build a mod now and make Command Code do anything you want.
🎬
视频
25732 粉丝
Mods are more powerful than plugins.
Command Code can build mods and modify any behavior from programmatic hooks to a completely different inference provider.
We bet you haven’t experienced something as powerful before.
Build a mod now and make Command Code do anything you want.
中文: 模组比插件更强大。
Command Code 可以构建模组,并将从编程钩子到完全不同的推理提供程序的任何行为进行修改。
我们以为你以前从未体验过那么强大的东西。
立即构建一个模组,让命令代码做到任何你想做的事情。
🎬
视频
25732 粉丝
Read docs to learn more: https://commandcode.ai/docs/mods
中文: 阅读文档以了解更多信息:
25732 粉丝
RT @theCTO: something is not normal with @CommandCodeAI
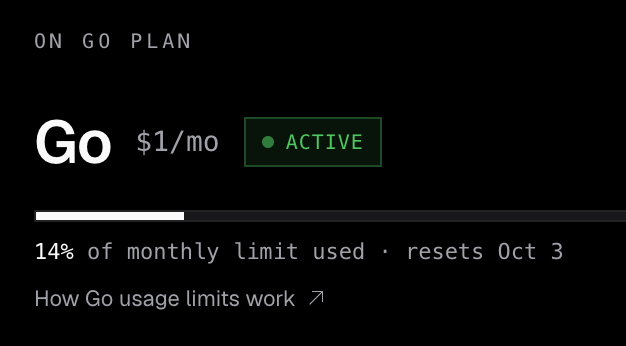
I refactored our entire docs and only used 14% of the monthly limits
you're insane @MrAhmadAwais https://twitter.com/theCTO/status/2099252870570983694/photo/1
中文: RT @theCTO:使用 @CommandCodeAI 来说某事并不正常
我重构了整个文档,仅使用了月度限值的14%
你疯了 @MrAhmadAwais
25732 粉丝
Last week these models went live in Command Code.
DeepSeek V4.1 Flash
Muse Spark 1.3 (with max reasoning)
Ling 3.0 Flash Sante (free model)
🐐
中文: 上周,这些模型在《命令代码》中上线了。
深度寻找V4.1闪存
缪斯·斯帕克 1.3(具有最大推理能力)
灵3.0闪光灯(免费型号)
🐐
25732 粉丝
DeepSeek is back, folks.
中文: DeepSeek 回来了,伙计们。
25732 粉丝
DeepSeek upstream is currently experiencing an unexpected downtime. We're working with them to help figure things out.
Please bear with us. Will report back as things go back to normal.
中文: DeepSeek上游目前正在经历意外的停机时间。我们正在与他们合作,帮助解决问题。
请忍受我们。随着情况恢复正常,会重新报告。
25732 粉丝
Share what you built with DeepSeek V4.1 Flash.
中文: 分享你使用 DeepSeek V4.1 Flash 构建的内容。
25732 粉丝
Command Code has built-in herdr support now! 🐐
中文: Command Code 现已内置 Sherd 支持!🐐
25732 粉丝
Extending $60 usage on DeepSeek V4.1 flash to 10 days. 🐐
中文: 将 DeepSeek V4.1 闪存的 60 美元使用时间延长至 10 天。🐐
25732 粉丝
RT @MrAhmadAwais: This is happening “the boon in using open models for cost savings” is real.
Just four months ago we launched @CommandCodeAI coding agent built specifically for open models.
60T tokens scale and 43K paying active customers later, more than 90% of our usage is open models.
In the first 24hrs of DeepSeek V4.1 launch, Command Code processed 3.1T paid tokens that’s 3x more than entire market on OpenRouter.
1T tokens on SOTA Claude/GPT cost you ~$5M
1T tokens on SOTA open models cost you
~$50K
I’m not joking. I’m literally looking at our data. These numbers are real.
That’s 100 times cheaper. While nearly as good. Run twice as many.
I believe top ten open models collectively beat single SOTA Claude/GPT model.
And when you discover a workflow that works for you, there’s literally nothing stopping you. You are not bound by subscription subsidies. Regular API prices are ten times or more manageable.
In near future, enterprise will wake up to this. Better, faster, cheaper, private, and available now!!
中文: RT @MrAhmadAwais:这种情况正在发生“利用开放式模型节省成本的福音”是真实的。
四个月前,我们推出了专为开放模型构建的 @CommandCodeAI 编码代理。
60T代币规模和43K付费活跃客户,之后我们使用的90%以上为开放模式。
在 DeepSeek V4.1 发布前24小时内,Command Code 处理了 3.1T 付费代币,该代币在 OpenRouter 上比整个市场多出 3 倍。
SOTA Clauda/GPT 上的 1T 代币售价约500万美元
SOTA 开放模型上的 1T 代币价格
约5万美元
我不是在开玩笑。我实际上是在查看我们的数据。这些数字是真实的。
便宜了100倍。虽然几乎一样好。跑两倍。
我相信十大开放型车型总体上超过了单款SOTA Clauda/GPT车型。
当你发现一个适合你的工作流程时,实际上并没有什么能阻挡你。您不受订阅补贴的约束。常规API价格是十倍或更易于管理的。
在不久的将来,企业会意识到这一点。更好、更快、更便宜、私密且现已推出!
25732 粉丝
DeepSeek V4.1 is our new top model. It’s used more in Command Code than anywhere else!!
中文: DeepSeek V4.1 是我们的新顶级型号。它在命令代码中的使用比其他任何地方都多!!
25732 粉丝
RT @MrAhmadAwais: DeepSeek V4.1 Flash, first 24 hours of launch, broke all records!!
Command Code served 3.1 TRILLION paid tokens. More than OpenRouter, OpenCode etc, or anyone else in the world.
Sustained 230-300 TPS.
Better, faster, cheaper!! 🐐 https://twitter.com/MrAhmadAwais/status/2098600014444638368/photo/1
中文: RT @MrAhmadAwais:DeepSeek V4.1 Flash,发布首播24小时,打破了所有纪录!!
Command Code 提供了 3.1 万付费代币。比 OpenRouter、OpenCode 等,或世界上任何其他人都多。
持续230-300 TPS。
更好、更快、更便宜!🐐

25732 粉丝
RT @CommandCodeAI: Ran FlappyBench on DeepSeek V4.1-Flash, GLM 5.3, and Kimi K3 with the same /design prompt.
🔹 DSV4.1-Flash: 9/10 · $0.0089 one-shot with the lowest cost
🔹 GLM-5.3: 9.5/10 · $0.0184 · nailed the UI but cost 2x more
🔹 Kimi K3: 8/10 · $0.0740 · hard-coded gameplay and 8x more https://twitter.com/CommandCodeAI/status/2098425878955110603/video/1
中文: RT @CommandCodeAI:使用相同的 /design 提示,在 DeepSeek V4.1-Flash、GLM 5.3 和 Kimi K3 上运行 FlappyBench。
🔹 DSV4.1-Flash:9/10 · 0.0089美元,单次射价最低
🔹 GLM-5.3:9.5/10 · 0.0184美元 · 确定用户界面,但价格要高 2 倍
🔹 基米 K3:8/10 · 0.0740美元 · 硬编码游戏玩法及更多
🎬
视频
25732 粉丝
Our engineering and design team has been testing 26+ side-by-side comparisons across frontier and open models. All runs are public and open source. Benchmark for this demo here:
https://github.com/CommandCodeAI/slash-design-showcase/tree/main/flappy-bird
中文: 我们的工程与设计团队一直在前沿和开放式模型上测试26个并排对比。所有运行均为公开和开源。此演示的基准:
25732 粉丝
Ran FlappyBench on DeepSeek V4.1-Flash, GLM 5.3, and Kimi K3 with the same /design prompt.
🔹 DSV4.1-Flash: 9/10 · $0.0089 one-shot with the lowest cost
🔹 GLM-5.3: 9.5/10 · $0.0184 · nailed the UI but cost 2x more
🔹 Kimi K3: 8/10 · $0.0740 · hard-coded gameplay and 8x more https://twitter.com/CommandCodeAI/status/2098425878955110603/video/1
中文: 使用相同的 /design 提示,在 DeepSeek V4.1-Flash、GLM 5.3 和 Kimi K3 上运行 FlappyBench。
🔹 DSV4.1-Flash:9/10 · 0.0089美元,单次射价最低
🔹 GLM-5.3:9.5/10 · 0.0184美元 · 确定用户界面,但价格要高 2 倍
🔹 基米 K3:8/10 · 0.0740美元 · 硬编码游戏玩法及更多
🎬
视频
25732 粉丝
RT @CommandCodeAI: DeepSeek V4.1 Flash now has 230-300 TPS enjoy the speed! 🐐
25732 粉丝
DeepSeek V4.1 Flash now has 230-300 TPS enjoy the speed! 🐐
中文: DeepSeek V4.1 Flash 现在拥有 230-300 TPS 享受速度!🐐
25732 粉丝
RT @CommandCodeAI: DeepSeek V4.1 Flash is live in Command Code.
6x usage on $10/mo GOAT for a week.
$60 usage. 154K requests. 7.8B tokens.
GOAT plan is the best AI coding plan.
Available in all plans and API.
🐐
中文: RT @CommandCodeAI:DeepSeek V4.1 Flash 以命令代码为实时版本。
每周使用10美元/月的GOAT6次。
使用费60美元。15.4万个请求。7.8B 代币。
GOAT 计划是最好的人工智能编程计划。
可在所有计划和API中使用。
🐐
25732 粉丝
RT @MrAhmadAwais: Command Code is now at 43 trillion tokens scale! 🐐
中文: RT @MrAhmadAwais:命令代码现在已达到43万亿枚代币规模!🐐
25732 粉丝
RT @CommandCodeAI: DeepSeek V4.1 Flash is live in Command Code.
6x usage on $10/mo GOAT for a week.
$60 usage. 154K requests. 7.8B tokens.
GOAT plan is the best AI coding plan.
Available in all plans and API.
🐐
中文: RT @CommandCodeAI:DeepSeek V4.1 Flash 以命令代码为实时版本。
每周使用10美元/月的GOAT6次。
使用费60美元。15.4万个请求。7.8B 代币。
GOAT 计划是最好的人工智能编程计划。
可在所有计划和API中使用。
🐐
25732 粉丝
DeepSeek V4.1 Flash is GOAT 🐐 https://twitter.com/CommandCodeAI/status/2098002287188922372/photo/1
中文: DeepSeek V4.1 闪存是 GOAT 🐐

25732 粉丝
@deepseek_ai GOAT model, we shipped it live in @CommandCodeAI with $60 usage in $10/mo GOAT plan.
It's #3 atm, but got a feeling it will be #1 model by the end of the day!!
https://x.com/CommandCodeAI/status/2097935455165850002
25732 粉丝
DeepSeek V4.1 Flash is live in Command Code.
6x usage on $10/mo GOAT for a week.
$60 usage. 154K requests. 7.8B tokens.
GOAT plan is the best AI coding plan.
Available in all plans and API.
🐐
25732 粉丝
Exciting DeepSeek x Command Code update landing soon. 🐐
中文: 令人兴奋的 DeepSeek x 命令代码更新即将登陆。🐐
25732 粉丝
RT @CommandCodeAI: Ling 3.0 Flash Sante is now free in Command Code.
5.1B active params. all subs. all plans
npm i -g command-code@latest
🐐
中文: RT @CommandCodeAI:Ling 3.0 Flash Sante 现已在命令代码中免费。
5.1B 正装参数。所有子。所有计划
npm i -g 命令代码@latest
🐐
25732 粉丝
Ling 3.0 Flash Sante is now free in Command Code.
5.1B active params. all subs. all plans
npm i -g command-code@latest
🐐
中文: Ling 3.0 Flash Sante 现已在命令代码中免费。
5.1B 正装参数。所有子。所有计划
npm i -g 命令代码@latest
🐐
25732 粉丝
Excited to partner up with @novita_labs to bring y'all this free model.
中文: 很高兴能与@novita_labs合作,为大家带来这款免费模型。
25732 粉丝
GOAT > Go → more GOAT customers than Go now. 🐐
25732 粉丝
The /fork command creates a new session from the current one with the same context. https://twitter.com/CommandCodeAI/status/2097158986323919090/video/1
中文: /fork 命令从当前上下文创建一个新会话。
🎬
视频
25732 粉丝
RT @CommandCodeAI: Muse Spark 1.3 Max is live in Command Code.
New reasoning effort param for harder problems and frontier performance.
Run /model, select Muse Spark 1.3
Then choose max for reasoning effort
中文: RT @CommandCodeAI:Muse Spark 1.3. Max 以命令代码为名。
新的推理能力,以解决更困难的问题和前沿表现。
运行/模型,选择Muse Spark 1.3%
然后选择 max 进行推理
25732 粉丝
Muse Spark 1.3 Max is live in Command Code.
New reasoning effort param for harder problems and frontier performance.
Run /model, select Muse Spark 1.3
Then choose max for reasoning effort
25732 粉丝
RT @CommandCodeAI: Next week. Hello, Desktop.
中文: RT @CommandCodeAI:下周。你好,桌面版。
25732 粉丝
Next week. Hello, Desktop.
中文: 下周。你好,桌面版。
25732 粉丝
GPT-6 Astra is live in Command Code.
中文: GPT-6 Astra 以命令代码为生。
25732 粉丝
Connect to MCP servers to query data, use tools and automate workflows. https://twitter.com/CommandCodeAI/status/2095924724702531999/video/1
中文: 连接到MCP服务器以查询数据、使用工具并实现工作流程自动化。
🎬
视频
25732 粉丝
everyone using open models today https://twitter.com/CommandCodeAI/status/2095568442925703478/photo/1
中文: 今天使用开放模型的每个人都在
25732 粉丝
Qwen 3.8 Max 0902 is now live in Command Code.
It's an upgraded Qwen 3.8 Max:
· 2.4T params
· 1M context
· Post-trained on coding & cowork
Available on GOAT, Pro, Max and API
中文: Qwen 3.8 Max 0902 现已进入命令代码。
升级版Qwen 3.8 Max:
2.4T 参数
1M 上下文
编程和编程后培训;编人
可在 GOAT、Pro、Max 和 API 上使用
25732 粉丝
claude codex down? switch to open models, we got you! 🐐
中文: 低调的密码?切换到开放式模型,我们找到了!🐐
25732 粉丝
RT @CommandCodeAI: Ran FlappyBench on Muse Spark 1.3, Gemini 3.8 Flash, and Grok-4.6 with the same /design prompt.
🔹 Muse Spark 1.3: 9/10 · $0.072. Nailed UI in 2 iterations with lowest cost
🔹 Grok-4.6: 9/10 · $0.095 · Matched Muse’s output, but cost 2x more
🔹 Gemini 3.8 Flash: 7/10 · $0.205 · Most expensive and not fully finished
中文: RT @CommandCodeAI:使用相同的 /design 提示,在 Muse Spark 1.3、Gemini 3.8 Flash 和 Grok-4.6 上运行 FlappyBench。
🔹 缪斯火花 1.3:9/10 · 0.072美元。以最低成本在两个版本中钉上UI
🔹 Grok-4.6:9/10 · 0.095美元 · 匹配的Muse输出,但价格高出2倍
🔹 Gemini 3.8 闪光灯:7/10 · 0.205 美元 · 最贵且尚未完全完成
🎬
视频
25732 粉丝
Our engineering and design team has been testing 26+ side-by-side comparisons across frontier and open models. All runs are public and open source. Benchmark for this demo here:
https://github.com/CommandCodeAI/slash-design-showcase/tree/main/flappy-bird
中文: 我们的工程与设计团队一直在前沿和开放式模型上测试26个并排对比。所有运行均为公开和开源。此演示的基准:
25732 粉丝
Ran FlappyBench on Muse Spark 1.3, Gemini 3.8 Flash, and Grok-4.6 with the same /design prompt.
🔹 Muse Spark 1.3: 9/10 · $0.072. Nailed UI in 2 iterations with lowest cost
🔹 Grok-4.6: 9/10 · $0.095 · Matched Muse’s output, but cost 2x more
🔹 Gemini 3.8 Flash: 7/10 · $0.205 · Most expensive and not fully finished
中文: 使用相同的 /design 提示,在 Muse Spark 1.3、Gemini 3.8 Flash 和 Grok-4.6 上运行 FlappyBench。
🔹 缪斯火花 1.3:9/10 · 0.072美元。以最低成本在两个版本中钉上UI
🔹 Grok-4.6:9/10 · 0.095美元 · 匹配的Muse输出,但价格高出2倍
🔹 Gemini 3.8 闪光灯:7/10 · 0.205 美元 · 最贵且尚未完全完成
🎬
视频
25732 粉丝
RT @CommandCodeAI: Meta Muse Spark 1.3 Contributor now live in Command Code.
Most capable lowest cost model yet.
Opus 5 & GPT 5.6 Sol class benchmark results.
Available in GOAT, Pro, Max, & API.
中文: RT @CommandCodeAI:Meta Muse Spark 1.3 贡献者现在以命令代码为首。
迄今为止最有能力的低成本模型。
Opus 5 & GPT 5.6 Sol 类基准测试结果。
提供GOAT、Pro、Max和Apm等版本。
25732 粉丝
RT @MrAhmadAwais: Command Code crossed $15M run rate today.
we’re winning minds, hearts, and support from the developer community at an astronomical scale and momentum.
likely the fastest growing coding agent ever, and one of the largest buyers of open model tokens.
• $15M run rate
• 28 trillion tokens scale
• 34K paying customers
• 99%+ cache hit rates
• $10/mo GOAT AI coding plan
we're building the best coding agent for open models!
if you're excited about open models, we are a small team of exceptionally strong, principled engineers to push toward the speed of light: the absolute ceiling of what open models can do. Harness, inference, hardware, kernels, every last-mile optimization.
we're hiring. come build it with us. 🐐
中文: RT @MrAhmadAwais: 命令代码今天突破了1500万美元的运行费率。
我们以惊人的规模和势头赢得开发者社区的思想、心灵和支持。
可能是有史以来增长最快的编码代理,也是开放模型代币的最大买家之一。
• 1500万美元运行费率
• 28万亿枚代币规模
• 34K 付费客户
• 99% 以上缓存命都率
• 每月10美元的GOAT人工智能编程计划
我们正在为开放模型打造最佳的编码代理!
如果你对开放式模型感到兴奋,我们是一支规模特别强、原理强大的工程师团队,致力于推动光速:即开放模型所能实现的绝对极限。硬件、推理、硬件、内核,每一英里的优化。
我们正在招聘。来和我们一起建立它。🐐

25732 粉丝
The cat is out of the bag.
https://x.com/CommandCodeAI/status/2095204852305739884
25732 粉丝
Check out @alexandr_wang's thread on this.
Muse spark is one of the top five models in Command Code. 6T tokens already.
And it's going open source next week! 🐐
https://x.com/alexandr_wang/status/2095232916276260884
25732 粉丝
Meta Muse Spark 1.3 Contributor now live in Command Code.
Most capable lowest cost model yet.
Opus 5 & GPT 5.6 Sol class benchmark results.
Available in GOAT, Pro, Max, & API.
中文: Meta Muse Spark 1.3 贡献者现在以命令代码为首。
迄今为止最有能力的低成本模型。
Opus 5 & GPT 5.6 Sol 类基准测试结果。
提供GOAT、Pro、Max和Apm等版本。
25732 粉丝
RT @CommandCodeAI: LongCat-2.0 is now free in Command Code.
1.6T params. 1M context. 48B activate.
Available on all plans to all subscribers.
npm i -g command-code
🐐
中文: RT @CommandCodeAI:LongCat-2.0 现已在命令代码中免费。
1.6T 参数。1M 上下文。48B 激活。
所有订阅者可随时提供。
npm i -g 命令代码
🐐
25732 粉丝
Gemini 3.8 Flash is now available in Command Code GOAT with 4x usage.
🐐
中文: Gemini 3.8 Flash 现已在 Command Code GOAT 中提供,使用率为 4 倍。
🐐
25732 粉丝
LongCat-2.0 is now free in Command Code.
1.6T params. 1M context. 48B activate.
Available on all plans to all subscribers.
npm i -g command-code
🐐
中文: LongCat-2.0 现已在命令代码中免费。
1.6T 参数。1M 上下文。48B 激活。
所有订阅者可随时提供。
npm i -g 命令代码
🐐
25732 粉丝
Excited to partner up with @Meituan_LongCat to bring y'all this free model, their team is going to be hanging out in Command Code Discord server today, if y'all have any feedback.
https://commandcode.ai/discord
中文: 很高兴能与@Meituan_LongCat 合作,为大家带来这款免费模型,如果大家有任何反馈,他们的团队今天就将在Command Code Discord服务器中挂断。
25732 粉丝
Do you want another free model with Command Code?
中文: 您想要另一个带有命令代码的免费模型吗?
25732 粉丝
Fable 5.1 is now live in Command Code.
Claude's most advanced coding model. 75% cheaper cache reads.
Available on Max plans and API.
25732 粉丝
Introducing the GOAT plan 🐐
Command Code GOAT plan is the best low-cost coding plan on the market today.
- $10/mo to get $70 credits. 7x what you pay
- 30+ open weight and closed models
$1 Go got you started. GOAT gets you shipping.
Subscribe — be a GOAT.
25732 粉丝
We ran a test between the new Qwen3.8-Max, Opus 5 and GPT-5.6 Sol.
3 models. same prompt. one-shot with the /design command.
Reviewed gameplay features, UX/UI and cost.
🔹 Qwen3.8-Max → 9/10 · $0.0248
🔹 GPT-5.6 Sol → 9/10 · $0.150
🔹 Opus 5 → 8.5/10 · $0.253
Qwen3.8-Max is… https://twitter.com/CommandCodeAI/status/2084293498950590839/video/1
 共 2 项
🎬
视频
25732 粉丝
Qwen 3.8 Max is now live in Command Code Go.
… and it's going open weight!!
most importantly, next week open-weights of Qwen3.8-Max and Qwen3.8-27B will be released!
🔹 2.4T params MoE flagship
🔹 Input: $2 Output: $6
🔹 Cache: $0.25 / M tokens
3.8 is 20% cheaper than 3.7
25732 粉丝
GPT-5.6 Terra and Luna are 50% off in Command Code.
Get 2X requests for every dollar of credit you spend.
GPT-5.6 Luna:
- $0.10/M input, $0.60/M output tokens
- Available on all plans (Go, Pro, Max, Team)
GPT-5.6 Terra:
- $1/M input, $6/M output tokens
- Available on Pro, Max,… https://twitter.com/CommandCodeAI/status/2083542775115727333/photo/1

25732 粉丝
MiniMax M3 is now FREE in Command Code!
We're partnering up with MiniMax.
One of the best open models.
LIVE NOW
• all subscribers $1 Go, Pro, Max, Ultra
• June 15-17 till capacity lasts
HOW
$ npm i -g command-code
$ cmd /model MiniMax M3 (FREE)
What are you building? https://twitter.com/CommandCodeAI/status/2066577317762326634/photo/1
中文: MiniMax M3 现已免费使用命令代码!
我们正在与MiniMax合作。
最佳开放式模型之一。
立即生活
• 所有订阅用户 1 美元 购买、专业、最大、超大
• 6月15日至17日,直至产能持续
如何
$ npm i -g 命令代码
$ cmd /型号 MiniMax M3(免费)
你在建什么?

25732 粉丝
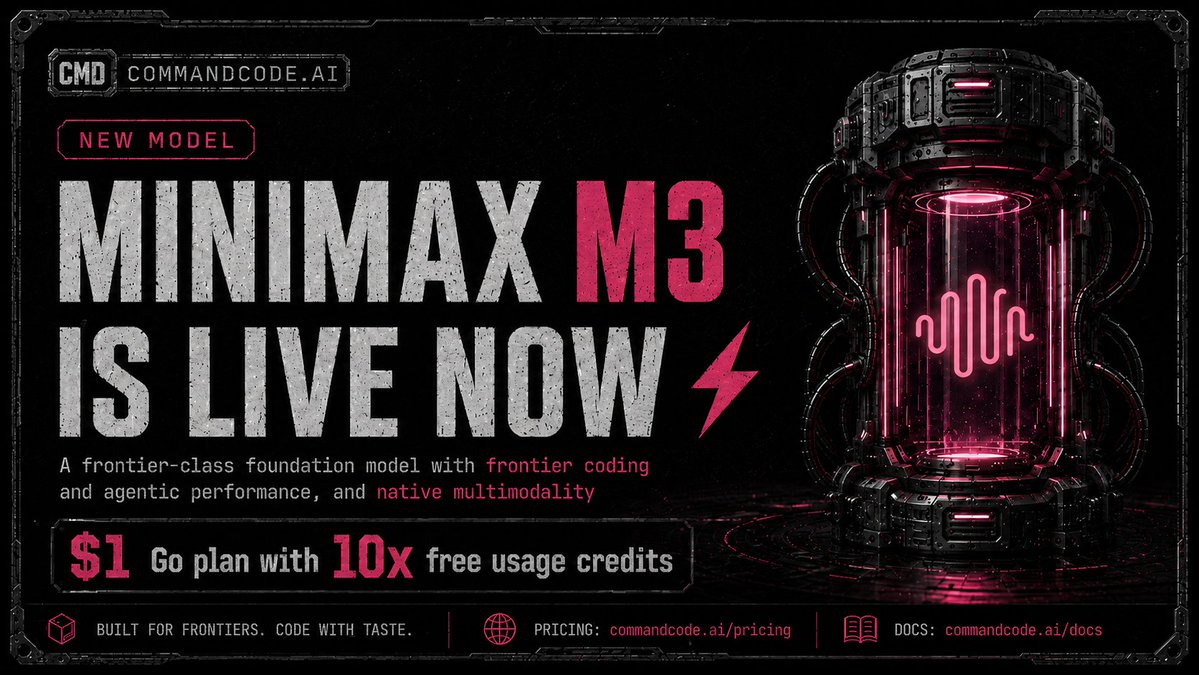
MiniMax M3 is live now on CommandCode!
A frontier-class open-weight model with 1M context, frontier coding, agentic performance, and native multimodality
Give it a try with our $1 Go plan with 10x free usage credits! https://twitter.com/CommandCodeAI/status/2061267713251848320/photo/1
中文: MiniMax M3 现已在 CommandCode 上上线!
具有1M上下文、前沿编码、代理性能和原生多态性的前沿开放量型
使用我们的1美元Go计划,提供10个免费使用积分,即可尝试!
25732 粉丝
A dollar for $40 of DeepSeek V4 Pro usage?
Hard to say no to that. https://twitter.com/CommandCodeAI/status/2057170407602688102/photo/1